GeneralBreaking NewsBreakingLatest News
CERT-In Issues Warning on Tata Motors' Connected Car Apps Over Security Flaws
Sentiment: NeutralHigh Priority
What Happened?
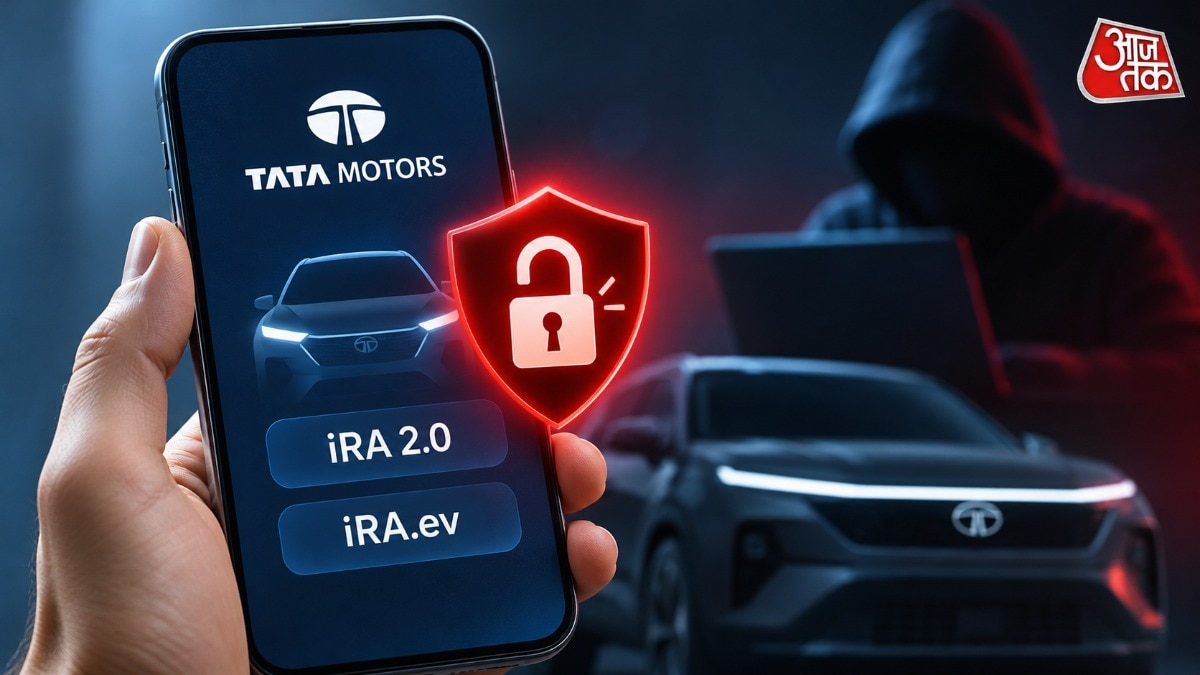
India's cybersecurity agency CERT-In has issued a warning regarding four security vulnerabilities in Tata Motors' connected car apps, iRA 2.0 and iRA.ev. These flaws could allow attackers to access sensitive user information.
Key points
- CERT-In identified four security vulnerabilities in Tata Motors' iRA 2.0 and iRA.ev apps.
- The vulnerabilities could allow attackers to create user identities and access sensitive information.
- The flaws are not in Tata cars themselves but in the apps.
- Users are advised to update their apps to the latest versions: iRA 2.0 to 26.8.2 and iRA.ev to 26.9.1.
- The vulnerabilities include issues with storing digital keys, WebView security, app logs, and SSL certificate pinning.
Key insights
- The vulnerabilities could lead to unauthorized access to vehicle-related services.
- Users may face privacy concerns if their identities are compromised.
- The incident underscores the need for robust cybersecurity measures in connected vehicle technologies.
Why it matters
This warning highlights the potential risks associated with connected car technologies and the importance of app security.
Entities
CERT-In· OrganizationTata Motors· CompanyiRA 2.0· ProductiRA.ev· Product
Source
India Today